


The Best FCP_FMG_AD-7.6 Exam Study Material and Preparation Test Question Dumps
Get Ready to Pass the FCP_FMG_AD-7.6 exam Right Now Using Our Fortinet Network Security Expert Exam Package
Fortinet FCP_FMG_AD-7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
NEW QUESTION # 37
Refer to the exhibits. An administrator needed to recover all the configurations related to the user, Support. The configurations were saved in configuration revision ID 9.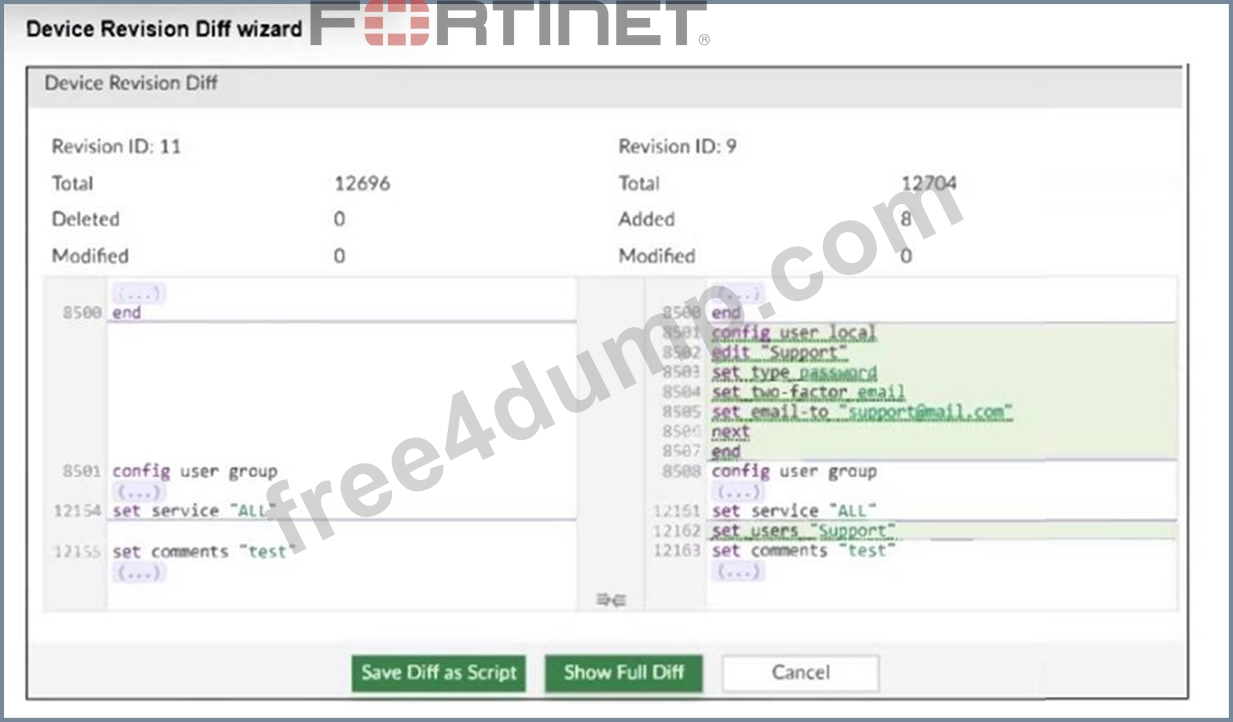
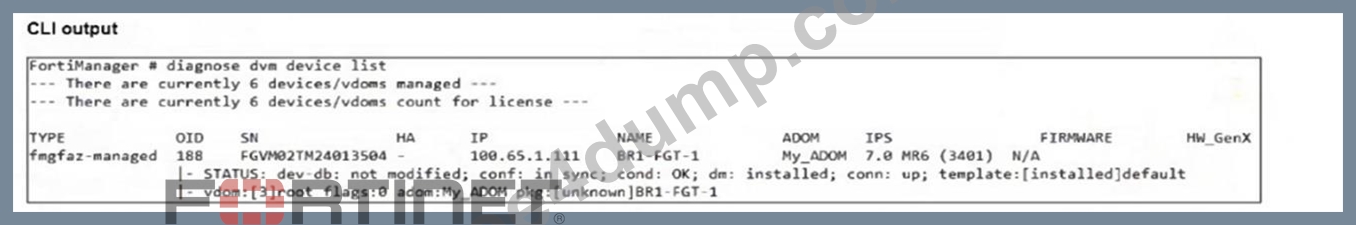
The administrator reverted the configuration using the Configuration Revision History window and received the CLI output shown in the exhibit.
What can you conclude from the CLI output?
- A. The administrator installed only the device-level configuration.
- B. The administrator reinstalled the policy package.
- C. The administrator set the flag to 0 to prevent configuration overrides.
- D. The administrator needs to retrieve the device to correctly detect the FortiGate firmware version.
Answer: A
Explanation:
Fortimanager will show the policy package as unknown when you do a retrieve or a revert revisions. The dev db is in sync, so the config was reverted and device settings installed.
NEW QUESTION # 38
Refer to the exhibit.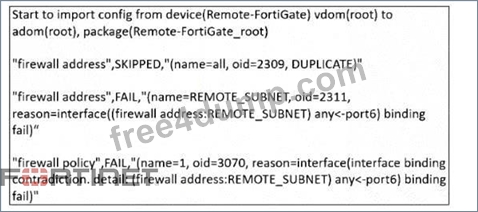
What can you conclude from the downloaded import report?
- A. The administrator will see a new policy package named Remote-FortiGate_root in the FortiManager ADOM database.
- B. As a result of this policy import process, FortiManager will create a new firewall address called REMOTE_SUBNET in the ADOM database.
- C. FortiManager does not support per-device mapping for firewall addresses.
- D. FortiManager will change the configuration of REMOTE_SUBNET to match the interface mapping coming in from Remote-FortiGate.
Answer: A
Explanation:
The import report shows that a new policy package named Remote-FortiGate_root will be created in the FortiManager ADOM database, but some firewall addresses and policies failed to import due to interface binding conflicts.
NEW QUESTION # 39
Which two items does an FGFM keepalive message include? (Choose two.)
- A. FortiGate IPS version
- B. FortiGate license information
- C. FortiGate uptime
- D. FortiGate configuration checksum
Answer: A,D
Explanation:
Keepalive messages, including the configuration checksums, are sent from FortiGate at configured intervals.
The messages also show the intrusion prevention system (IPS) version of the FortiGate device.
NEW QUESTION # 40
An administrator configures a new BGP peer in the FortiManager device-level database of FortiGate. They reinstall the policy package to the managed FortiGate device without any errors.
However, when the administrator logs in to FortiGate, they do not see the BGP configuration changes. What is the most likely reason why FortiManager did not push the BGP peer changes to FortiGate?
- A. The administrator must use the Install Wizard and select Install device settings only to push BGP settings
- B. The administrator must run a sanity check on FortiManager to make sure the database is not corrupted.
- C. The FortiGate firmware version is different from the FortiManager ADOM version.
- D. Fortigate has a BGP template assigned on the FortiManager database.
Answer: A
Explanation:
If you change BGP in FortiManager and only reinstall the policy package, the change will NOT reach FortiGate because BGP is a device setting. You must install device settings.
NEW QUESTION # 41
Refer to the exhibits.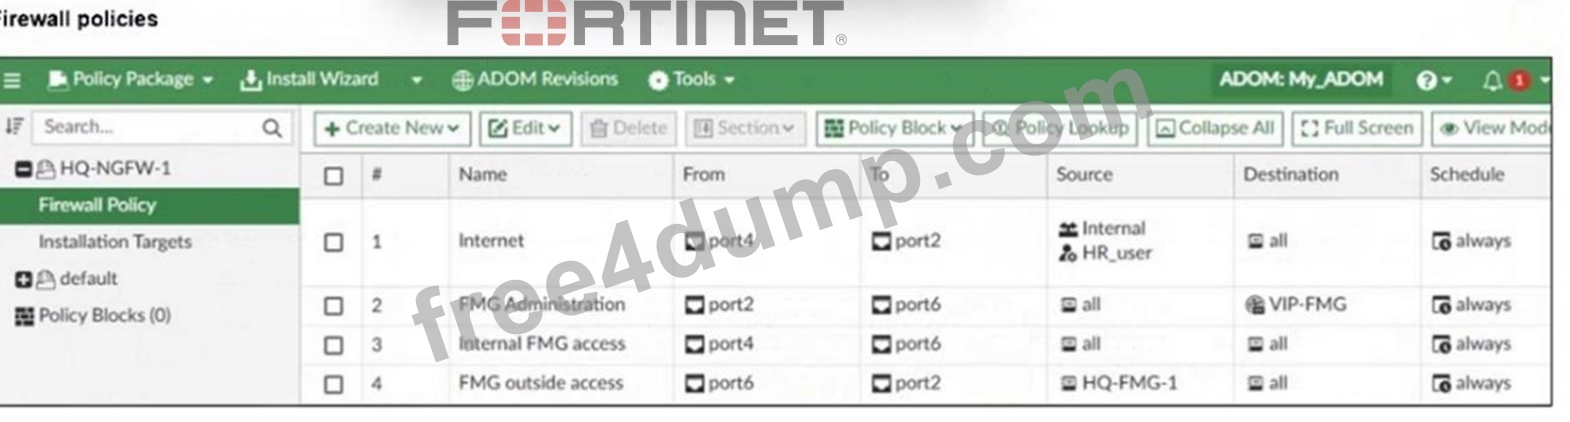
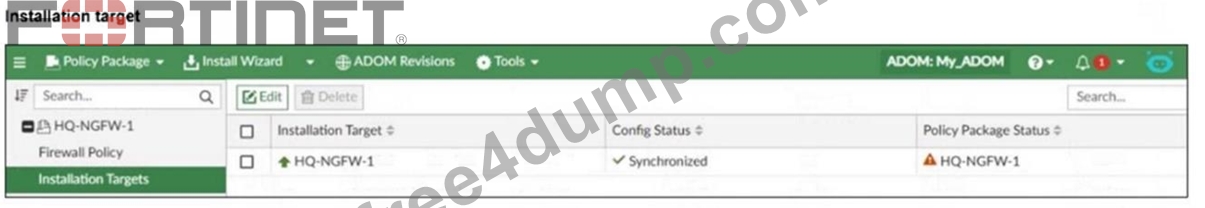
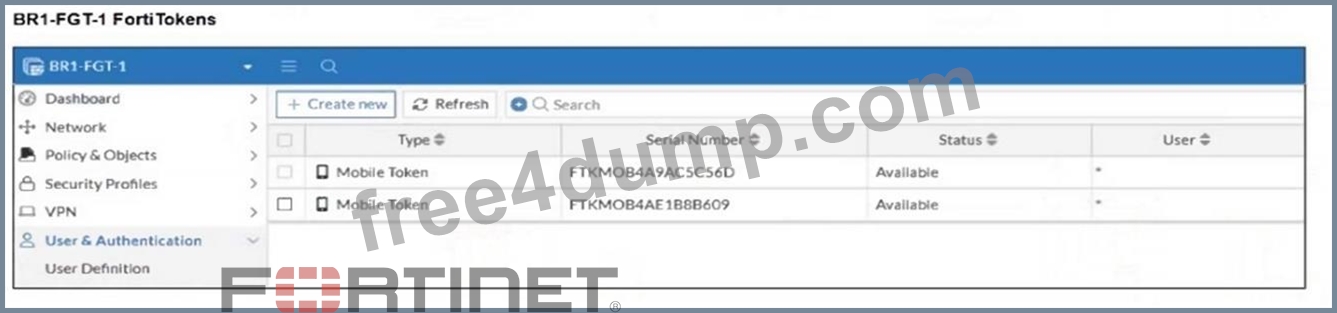
An administrator needs to push a FortiToken Mobile to assign it to HR_user in the HQ-NGFW-1.
However, when installing the policy package, they receive the following error message: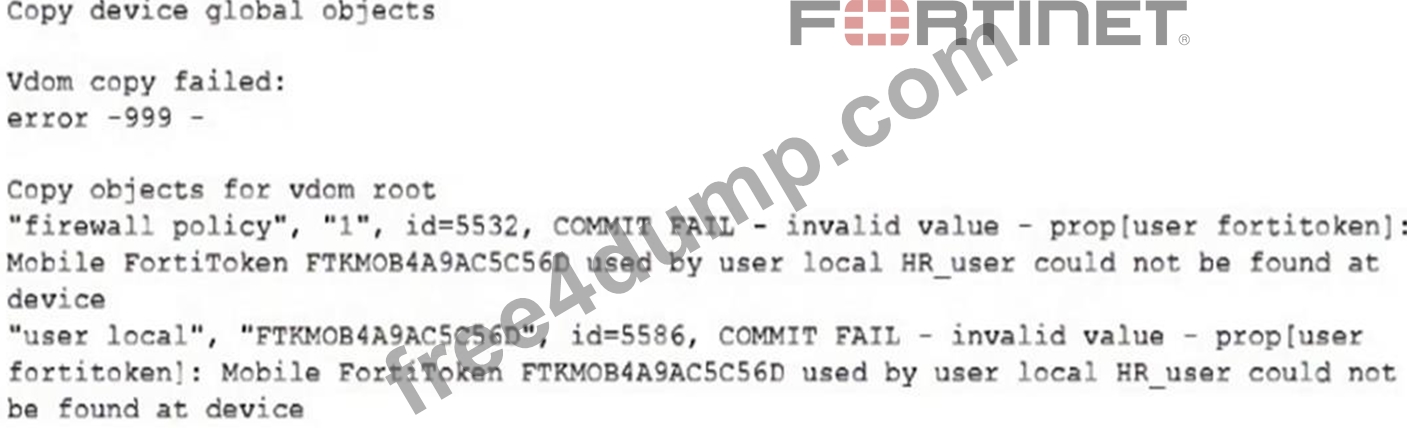
Why is the administrator not able to install the FortiToken on the HQ-NGFW-1 firewall?
- A. The administrator must use a metadata variable to assign the same FortiToken to multiple users in FortiManager.
- B. The administrator must use a user local meta field to assign FortiToken.
- C. The administrator must use per-device mapping to assign the FortiToken to HQ-NGFW-1.
- D. The administrator must use a valid FortiToken that exists on HQ-NGFW-1.
Answer: D
Explanation:
The error occurs because the FortiToken used (FTKM0B4A9AC5C56D) must already exist and be registered on the FortiGate device HQ-NGFW-1. FortiManager cannot push or create new FortiTokens on the device; the token must be valid and present on the FortiGate before it can be assigned to a user.
NEW QUESTION # 42
Refer to the exhibits.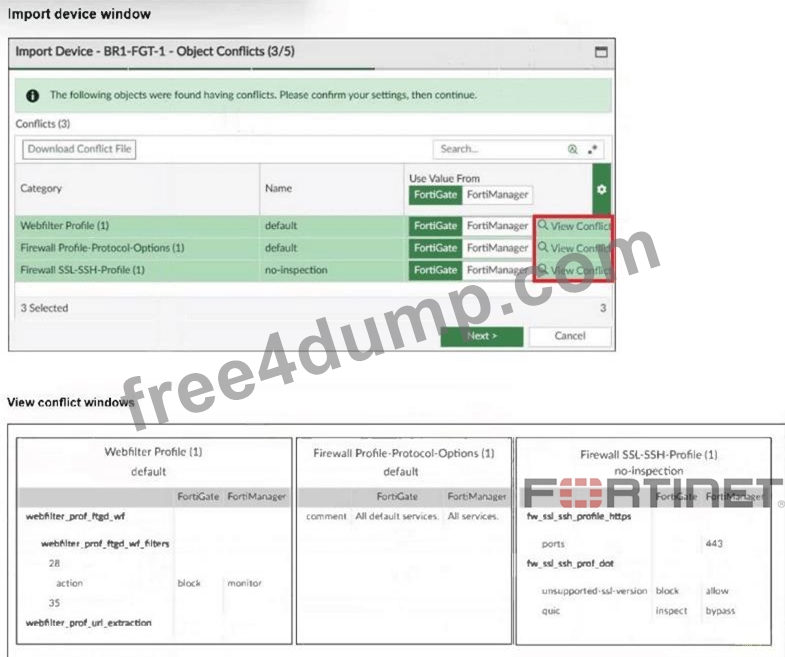
An administrator added BR1-FGT-1 to FortiManager and started importing the policy package. During the process, they saw that they need to choose values from FortiGate or FortiManager.
Which conclusion is most clearly supported by the exhibits?
- A. FortiManager has a different FortiGuard database compared to FortiGate BR1-FGT-1 for the QUIC protocol.
- B. BR1-FGT-1 does not support the SSL/SSH profile with HTTPS on port 443.
- C. The administrator must match the FortiOS firmware version with the FortiManager ADOM firmware version to resolve the conflict status.
- D. The default Firewall Profile-Protocol-Options object is the only profile that does not significantly affect any configuration changes on either FortiManager or FortiGate.
Answer: D
Explanation:
The exhibits are directly supported by the lab guide's troubleshooting section. It states: "The only profile that can be replaced is the Firewall Profile-Protocol-Options profile, because the only difference is a change in the comment field." It then explains that for the other two profiles, "Whether you accept the value from BR1-FGT-1 or FortiManager, it will cause changes on different devices." That exactly matches C . The conflict window is not primarily showing a firmware mismatch, and the guide does not say BR1-FGT-1 lacks HTTPS 443 support. It also does not describe this as a FortiGuard database mismatch for QUIC. Instead, the key point is that only the default Firewall Profile-Protocol-Options conflict is minor enough to safely take from FortiManager because the difference is only in the comment field
. The web filter and SSL/SSH profiles would cause real configuration differences if replaced.
NEW QUESTION # 43
Refer to the exhibits.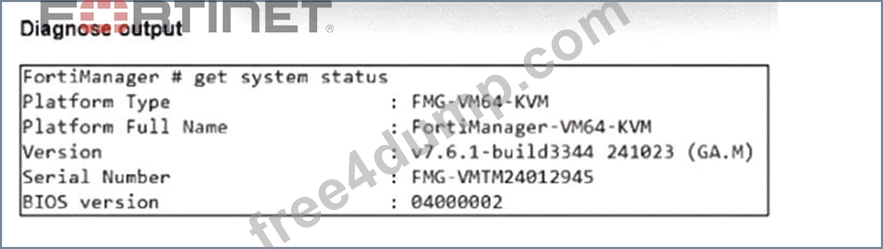
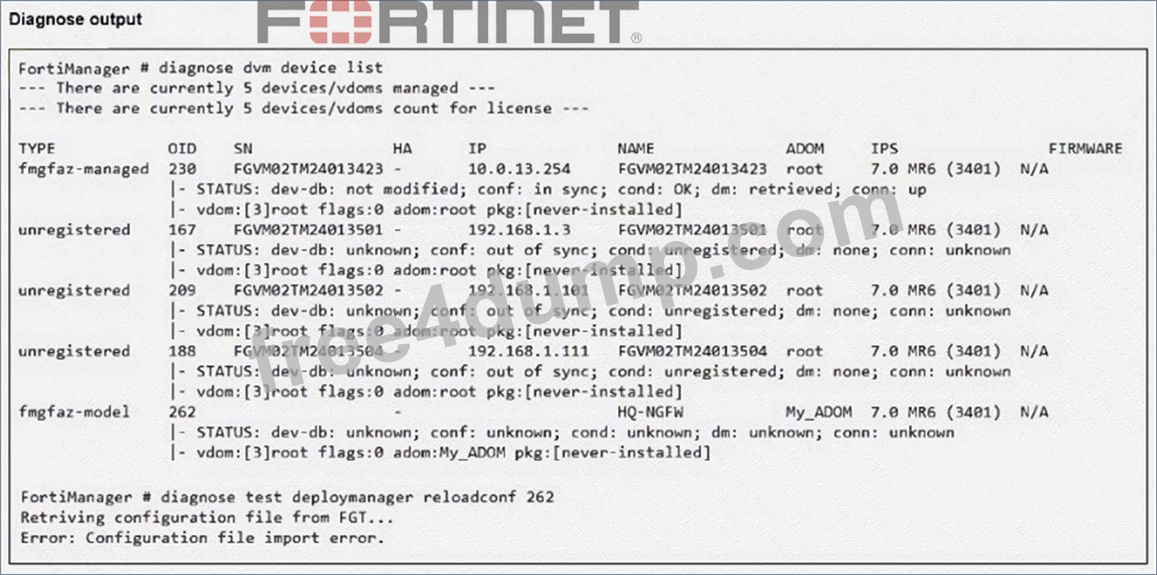
An administrator runs the reload failure commanddiagnose test deploymanager reloadconf 262on FortiManager.
Why does the administrator receive an error message?
- A. The administrator just recently added FortiGate HQ-NGFW as a model device.
- B. FortiManager requires the FortiGate serial number instead of the ID number.
- C. FortiManager does not support FortiOS version 7.0.
- D. The administrator must use the FortiGate name instead of the ID number.
Answer: A
Explanation:
The error occurs because the FortiGate HQ-NGFW device with ID 262 is a newly added model device and has not yet been fully synchronized or installed with a configuration package, which causes the reload configuration command to fail.
NEW QUESTION # 44
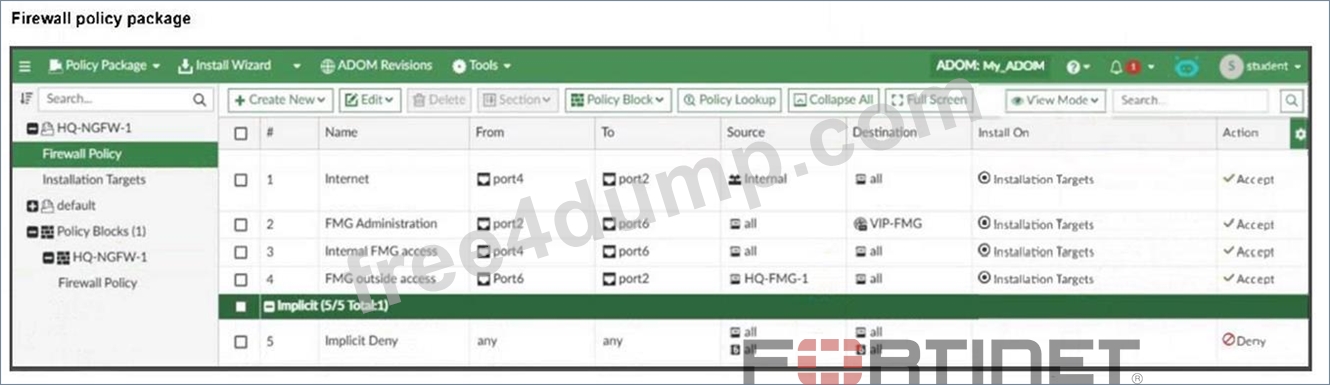
Refer to the exhibits. An administrator ran the Install Wizard and selected to install both the policy package and device settings.
Why can the administrator not install the policy package on HQ-NGFW-1?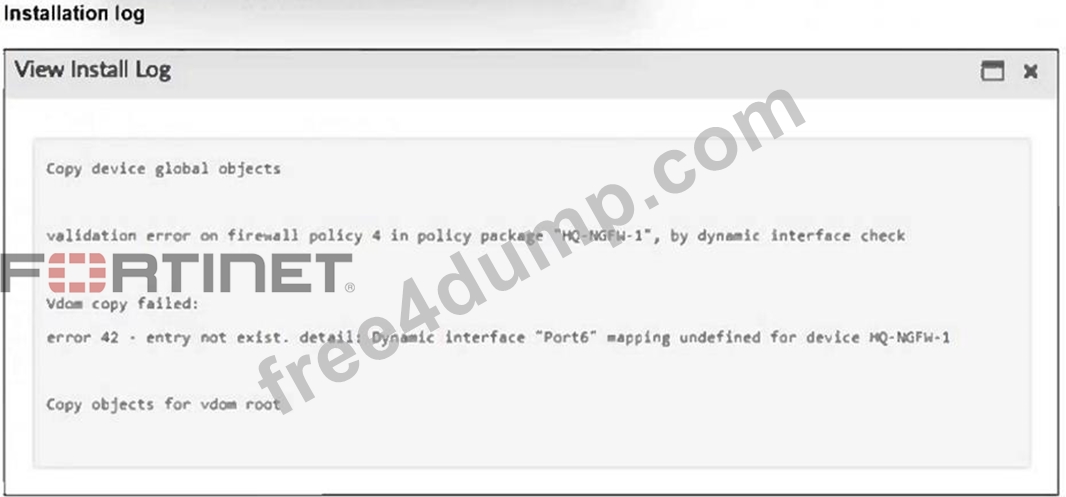
- A. The administrator must remove the policy block assigned to HQ-NFFW-1.
- B. The administrator must change the Install on column from Installation Targets to HQ-NGFW-1.
- C. The administrator must replace the interface Port6 with port6.
- D. The administrator must use the admin user to install the policy package.
Answer: C
Explanation:
Policy 4 has "Port6" in "From". The "P" in Port6 makes it a different interface. No the same than
"port6" with "p".
NEW QUESTION # 45
Refer to Exhibit: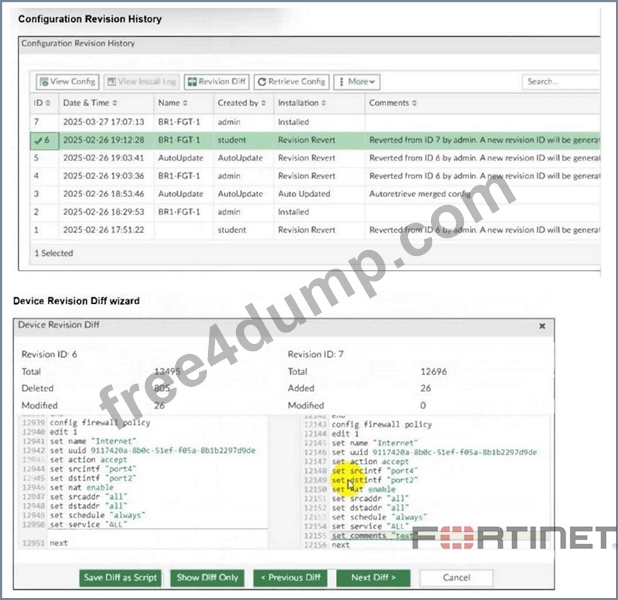
An administrator admin used the Configuration Revision History window to revert the FortiGate device configuration to revision ID 6. After running the reinstall policy package, the administrator noticed problems with the firewall policy- they could not see the unset comment on policy ID 1.
Why did FortiManager not remove the comment from policy ID 1 when the administrator ran reinstall policy package?
- A. Because every time the administrator uses the revert config file, they must use the Install Wizard instead of running the reinstall policy package.
- B. Because the administrator used the Revision Diff view, which shows what changed, not what will be installed.
- C. Because the administrator must import the firewall policies to update the firewall policy package.
- D. Because the administrator student must install the configuration changes to correctly see the expected results.
Answer: C
Explanation:
The correct answer is B . The FortiManager 7.6 Administrator Study Guide gives the exact extract:
"Performing a revert operation followed by an installation only reverts device-level changes and does not revert policy packages. To achieve full synchronization, you must run the Import Configuration tool on FortiManager to synchronize the policy package." The guide also states: "After every retrieve, auto-update, or revert operation, you must use Import Configuration to ensure the policy information is synchronized." In the exhibit, the missing unset comment for policy ID 1 is a policy package issue, not just a device-level revert issue. Reinstalling the existing policy package does not automatically rebuild it from the reverted revision. The administrator must import the firewall policies again so the policy package reflects the reverted policy state. That is why the comment was not removed.
=========
NEW QUESTION # 46
An administrator has assigned a global policy package to a new ADOM named ADOM1.
What will happen if the administrator tries to create a new policy package in ADOM1?
- A. The administrator will be able to select the option to assign the global policy package to the new policy package.
- B. FortiManager will automatically assign the global policy package to the new policy package.
- C. FortiManager will automatically install policies on the policy package in ADOM1.
- D. The administrator will have to assign the global policy package from the global ADOM.
Answer: A
Explanation:
When a global policy package is assigned to an ADOM, administrators creating new policy packages within that ADOM have the option to select and assign the global policy package to the new policy package if desired.
NEW QUESTION # 47
An administrator has assigned a global policy package to a new ADOM named ADOM1. What will happen if the administrator tries to create a new policy package in ADOM1?
- A. The administrator will be able to select the option to assign the global policy package to the new policy package.
- B. FortiManager will automatically assign the global policy package to the new policy package.
- C. FortiManager will automatically install policies on the policy package in ADOM1.
- D. The administrator will have to assign the global policy package from the global ADOM.
Answer: A
Explanation:
When a global policy package is assigned to an ADOM, administrators creating new policy packages within that ADOM have the option to select and assign the global policy package to the new policy package if desired.
NEW QUESTION # 48
An administrator created a new global policy package that includes both header policies and footer policies.
What two things must the administrator know before deploying the global policy package to ADOM2? (Choose two.)
- A. They can promote ADOM2 objects to global objects.
- B. They can synchronize policy packages by importing from the ADOM2 policy package into the global ADOM policy package.
- C. They can assign the global policy package to all or selected policy packaged within ADOM2.
- D. They must install from the ADOM2 layer to FortiGate when using the Automatically install policies to ADOM devices option.
Answer: A,C
Explanation:
Before deploying a Global Policy Package that uses shared objects, the administrator needs to ensure any objects created locally in the target ADOM (ADOM2) that they want to use in the global policies (header or footer) are available in the Global ADOM.
The Global Policy Package must be assigned to the specific Local Policy Packages within ADOM2 that are meant to inherit those global header and footer rules. The administrator can choose to assign the Global Policy Package to all policy packages in ADOM2 or only to selected ones.
NEW QUESTION # 49
What is the best explanation of how FortiManager helps with mass provisioning?
- A. It uses templates to configure the same settings on many devices simultaneously.
- B. It sends email alerts when new devices connect.
- C. It provides local FortiGuard Distribution Server (FDS) services to the network.
- D. It upgrades the OS of each FortiGate device.
Answer: A
Explanation:
FortiManager helps with mass provisioning by using templates that allow administrators to configure the same settings on multiple FortiGate devices simultaneously, streamlining deployment and management.
NEW QUESTION # 50
A FortiManager administrator has moved a FortiGate device to a new ADOM, but they cannot see the policy or object configurations for that FortiGate.
What should the administrator do to see the policy or object configurations?
- A. Use ADOM shared objects to restore all missing data.
- B. Reset the device and add it to the new ADOM again.
- C. Use ADOM sync to restore the missing configurations.
- D. Import the policy package manually using the Import Configuration wizard.
Answer: D
Explanation:
When a FortiGate device is moved from its original ADOM (Source ADOM) to a new ADOM (Target ADOM), only the Device Database (the device's running configuration) moves with it.
The Policy Package and the Policy/Object configurations are not automatically transferred because they are considered part of the Source ADOM's specific policy logic.
NEW QUESTION # 51
Refer to the exhibit. Which statement about the environment shown in the exhibit is true?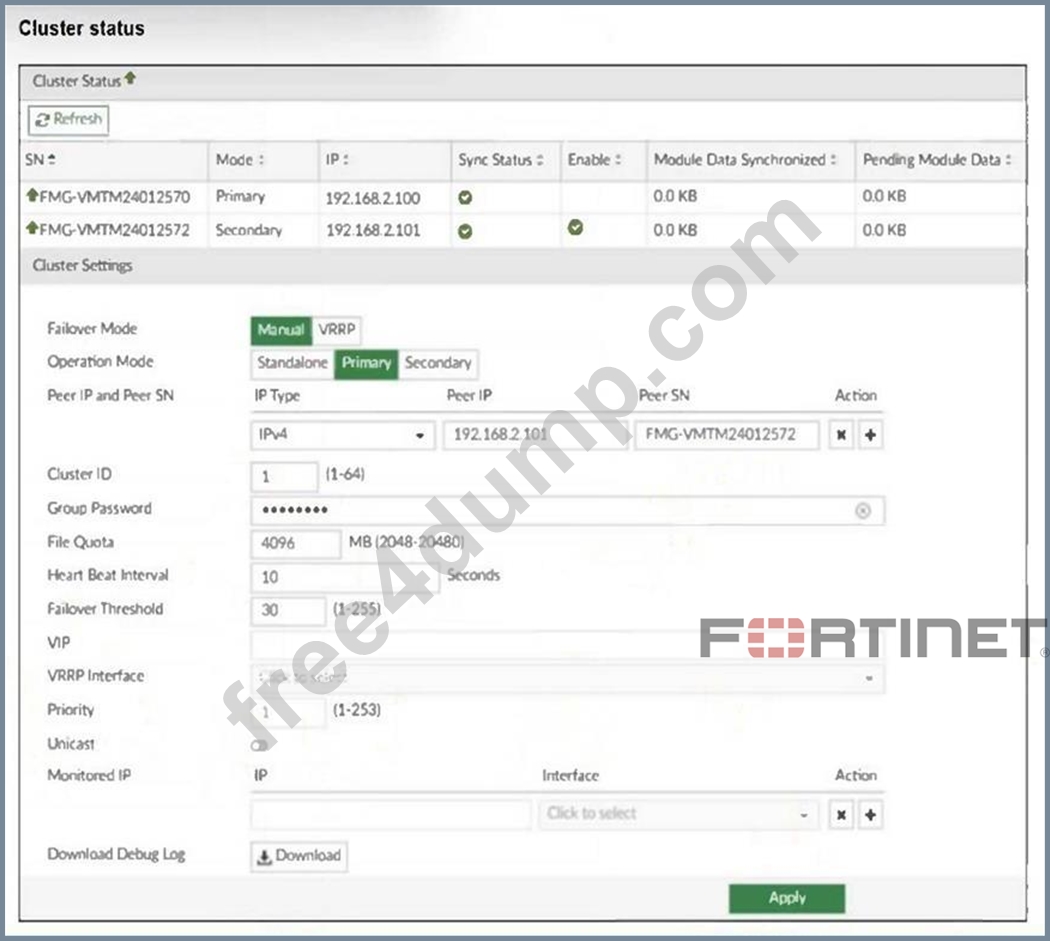
- A. A failover will take place after five minutes without receiving heartbeat packets.
- B. You must restart the secondary device if you promote it to primary.
- C. FortiAnalyzer features are not enabled on this FortiManager device.
- D. No FortiGuard packages have been synchronized between the cluster member.
Answer: C
Explanation:
HA is not supported if you have the FortiAnalyzer features enabled on FortiManager.
NEW QUESTION # 52
Refer to the exhibits.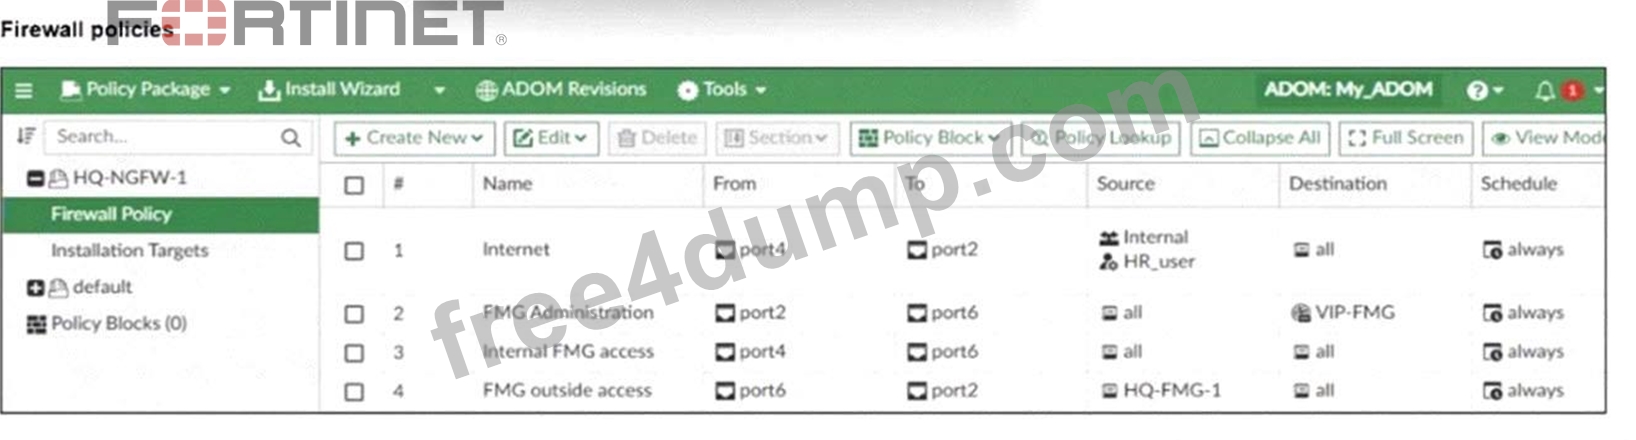
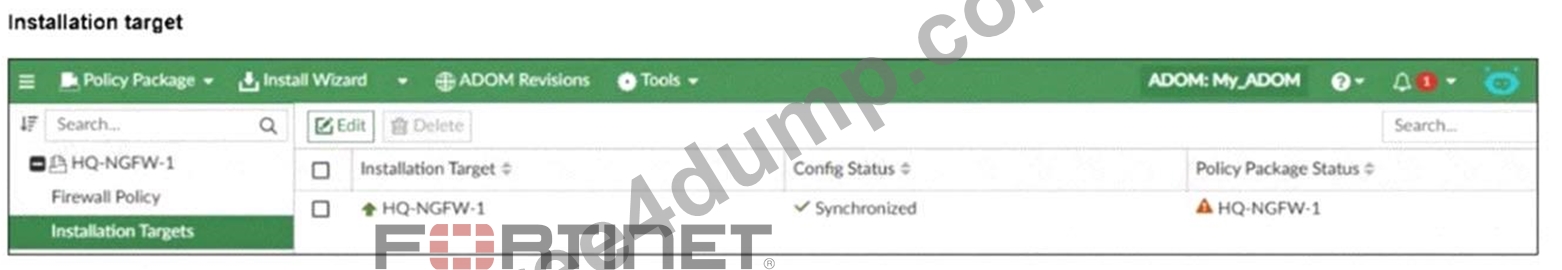
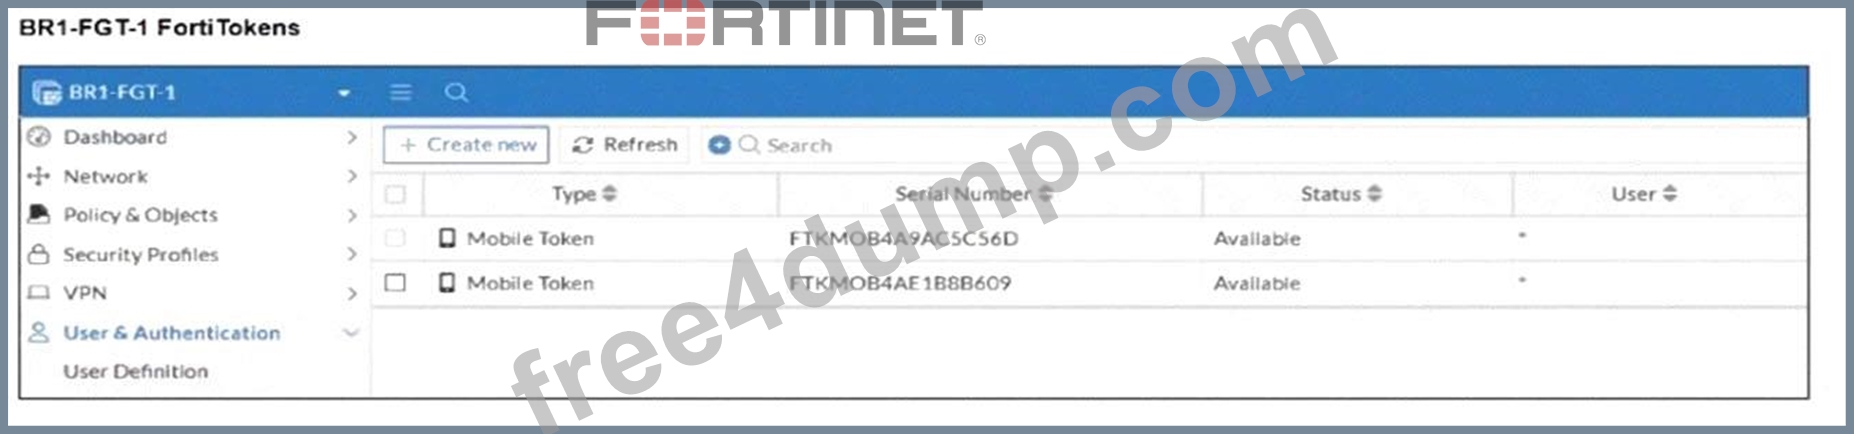
An administrator needs to push a FortiToken Mobile to assign it to HR_user in the HQ-NGFW-1.
However, when installing the policy package, they receive the following error message: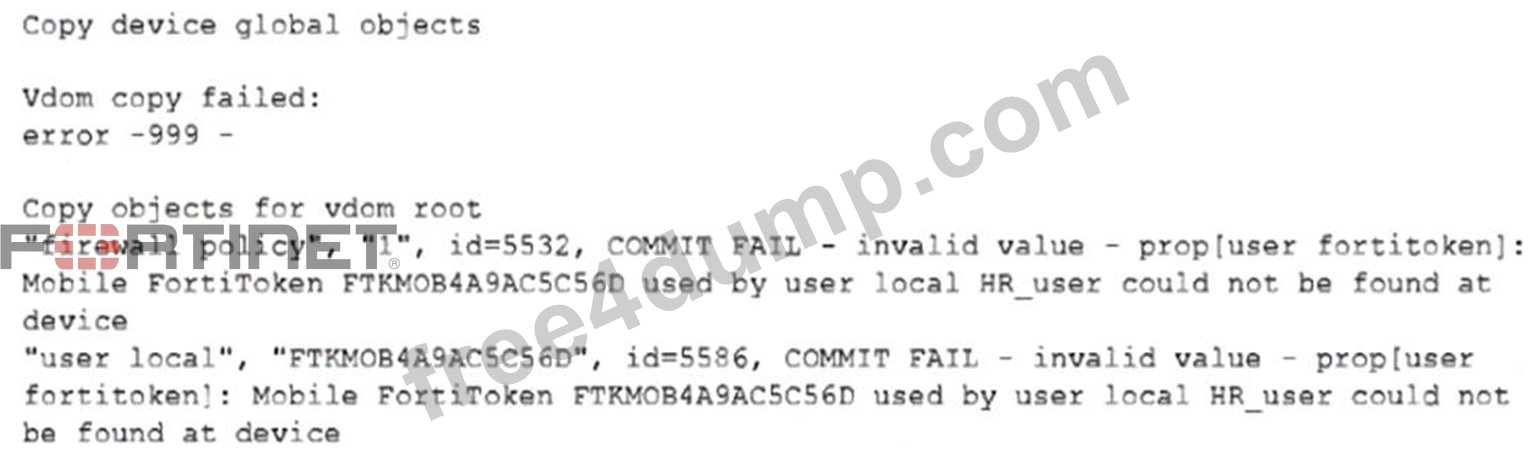
Why is the administratornotable to install the FortiToken on the HQ-NGFW-1 firewall?
- A. The administrator must use a metadata variable to assign the same FortiToken to multiple users in FortiManager.
- B. The administrator must use a user local meta field to assign FortiToken.
- C. The administrator must use per-device mapping to assign the FortiToken to HQ-NGFW-1.
- D. The administrator must use a valid FortiToken that exists on HQ-NGFW-1.
Answer: D
Explanation:
The error occurs because the FortiToken used (FTKM0B4A9AC5C56D) must already exist and be registered on the FortiGate device HQ-NGFW-1. FortiManager cannot push or create new FortiTokens on the device; the token must be valid and present on the FortiGate before it can be assigned to a user.
NEW QUESTION # 53
Refer to the exhibit. An administrator assigned a new policy package to FortiGate HQ-NGFW-1.
In the installation preview, they noticed some settings they did not modify and are unsure about the changes.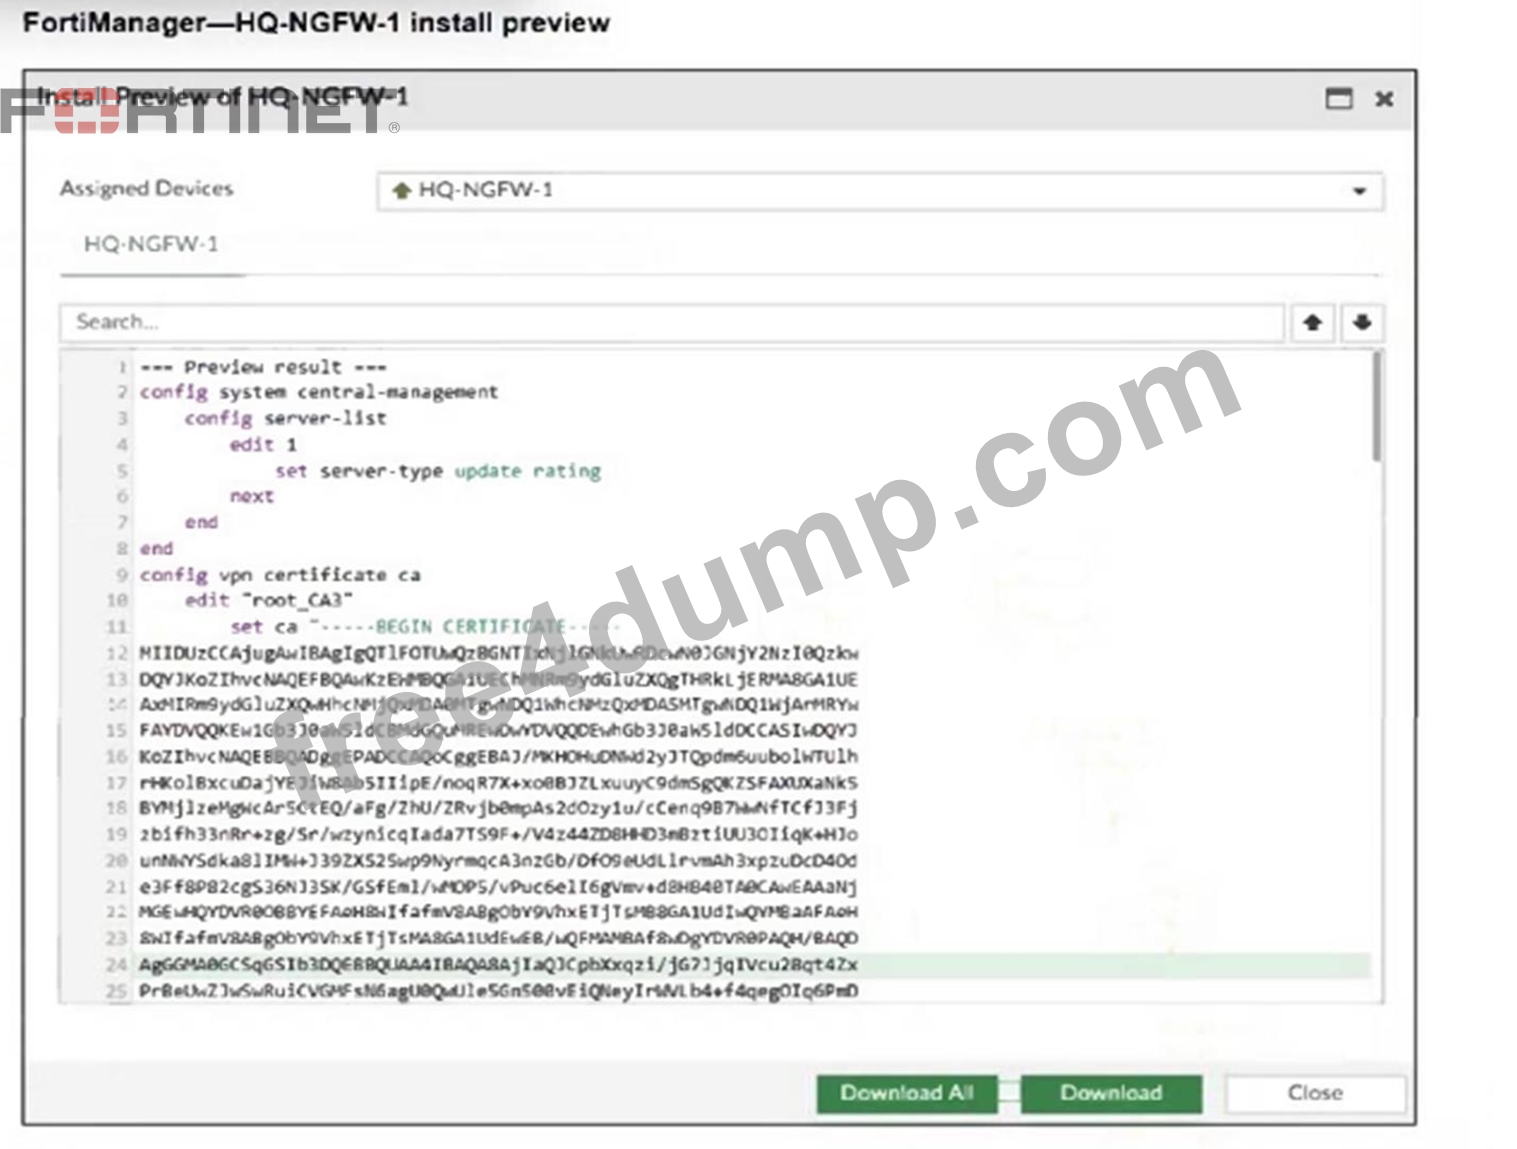
Based on the exhibit, which two things will happen if they continue with the installation? (Choose two.)
- A. FortiManager will install the CA certificate named root_CA3 to authenticate FortiGate-to- FortiManager communication protocol (FGFM) tunnel connections with FortiGate HQ- NGFW-1.
- B. FortiGate HQ-NGFW-1 can contact the FortiManager acting as FortiGuard Distribution Server (FDS) to download FortiGuard updates.
- C. FortiGate HQ-NGFW-1 can use FortiManager firmware templates to upgrade firmware and ratings.
- D. FortiGate HQ-NGFW-1 will use the root_CA3 certificate in firewall address objects or policies.
Answer: A,B
Explanation:
The configuration includes a server-list with server-type set to "update rating," which enables FortiGate HQ-NGFW-1 to contact FortiManager as a FortiGuard Distribution Server (FDS) for FortiGuard updates.
The installation includes a root_CA3 certificate, which FortiManager will install on FortiGate HQ- NGFW-1 to authenticate FGFM tunnel connections between the devices.
NEW QUESTION # 54
Refer to the exhibit.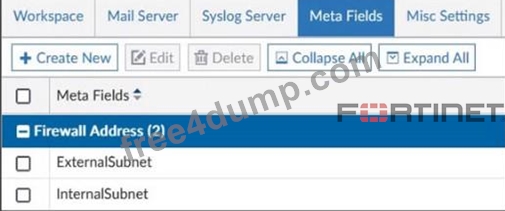
An administrator created two new meta fields in FortiManager.
Which operation can you perform with these parameters?
- A. You can add them to objects as custom attributes.
- B. You can export them to be used in other ADOMs.
- C. You can use them as variables in scripts.
- D. You can invoke them using the $ character.
Answer: A
Explanation:
Meta fields in FortiManager can be added to objects as custom attributes, allowing administrators to categorize and add additional information to firewall objects for easier management and identification.
NEW QUESTION # 55
While attempting to push a NetFlow configuration script through the FortiManager policy package:
an administrator encounters an error stating that an object is unrecognized in line 4.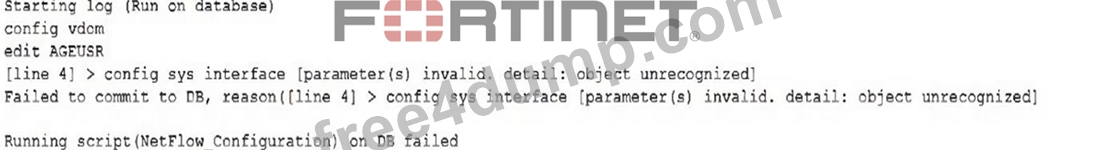
What must the administrator do to successfully apply the NetFlow configuration script and avoid the object unrecognized error?
- A. Run the script on the device database.
- B. Create a normalized interface on the policy layer before running the script.
- C. Make sure the user running the script has full access to the VDOM--AGEUSR.
- D. Use metadata variables if they use VDOMs in the script.
Answer: D
Explanation:
When using scripts that reference VDOM-specific objects, such as interfaces, in FortiManager, metadata variables must be used to correctly map those objects per VDOM. This prevents "object unrecognized" errors during script execution.
NEW QUESTION # 56
Refer to the exhibit. Which two statements about the output are true? (Choose two.)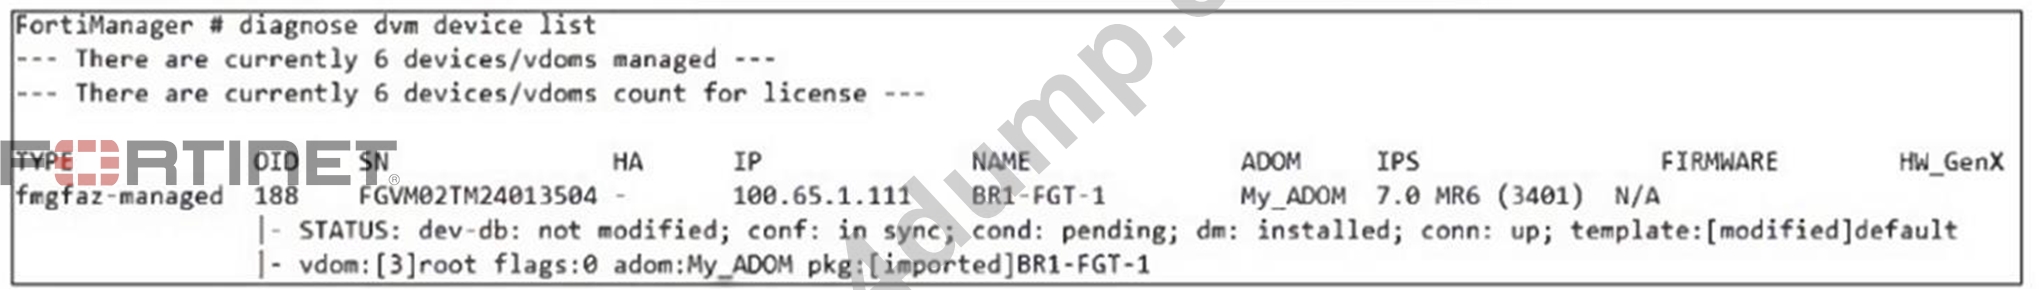
- A. Configuration changes have been installed on FortiGate, updating policy and device-level database.
- B. The system template default will override device-level database configurations.
- C. The latest revision history for the managed FortiGate does not match the device-level database.
- D. The latest revision history for the managed FortiGate does match the FortiManager policy database.
Answer: C,D
Explanation:
- conf: in sync - This is the sync status which shows that the latest revision history is in sync with Fortigate's configuration.
There is a new modification on FortiManager device level DB (dev-db: modified) which wasn't installed to FortiGate (cond: pending).
NEW QUESTION # 57
......
Get Special Discount Offer of FCP_FMG_AD-7.6 Certification Exam Sample Questions and Answers: https://surepass.free4dump.com/FCP_FMG_AD-7.6-real-dump.html